

What Happens If Third-Party Cookies Change Without You Knowing?
June 3, 2026
•

4 min read
Table of contents
back
to the top
What Happens If Third-Party Cookies Change Without You Knowing
Introduction
Websites often rely on third-party tools — analytics, marketing, chat, plugins — and most of them depend on cookies. But what happens when these cookies change purpose without your knowledge?
This blog explains why unmonitored third-party cookie changes can break your GDPR compliance, and how to stay ahead of them.
1. The Problem With “Silent Changes”
Third-party vendors regularly update their cookies:
- Names change
- Purposes shift (analytics → marketing)
- New domains appear
- Persistent identifiers evolve
These changes usually happen without notification.
If your cookie policy and consent categorization do not reflect these updates, your site becomes non-compliant.
2. Why Purpose Changes Matter
Under GDPR:
- Consent must be purpose-specific
- Users must know exactly why data is collected
If a cookie initially used for analytics later starts collecting targeting data, the original consent is no longer valid.
The consent no longer matches the cookie’s behavior.
3. Common Scenarios of Hidden Change
Examples of how cookies can change without you knowing:
- A vendor adds remarketing capabilities
- A plugin starts tracking cross-site behavior
- A service updates its SDK with new identifiers
- Cloud fonts or embeds drop new cookies
In every case, the real processing diverges from documented behavior.
4. Why Manual Audits Aren’t Enough
Relying on manual cookie lists fails because:
- Changes can happen daily
- Developers may not know about vendor backend updates
- Policies often go stale
- Users may have given consent to outdated purposes
Manual updates simply cannot keep pace.
5. How Cookie Scanners Prevent Compliance Breaks
Regular, automated cookie scanning:
- Detects new cookies
- Flags changed cookie purposes
- Matches behavior to consent categories
- Triggers CMP reconfiguration or re-consent
This ensures your consent catalog remains accurate and lawful.
Final Takeaway
Third-party cookies can change purpose without notice, invalidating past consent and risking GDPR violations. Ongoing scanning and accurate categorization are essential to maintain truth-in-labeling and stay audit-ready.
Sources
Explore further
Do A/B Testing Tools Require Cookie Consent?
A/B tests can store IDs, share events and feed ad audiences. Learn when experiments need consent, when a narrow exemption may apply and how to run tests without ignoring privacy.
October 22, 2026
9 min
Cookies, Local Storage and Session Storage: What Is the Difference?
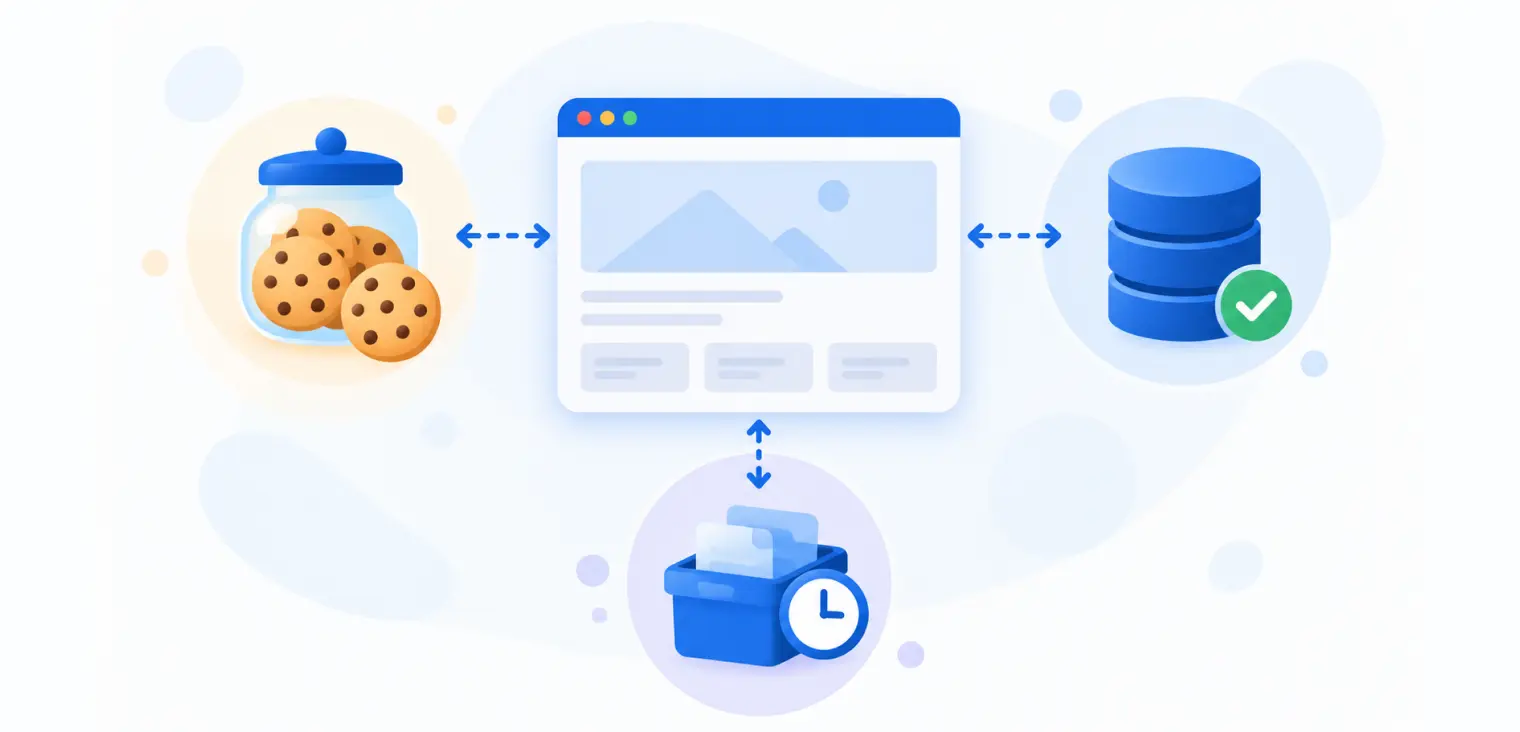
Cookies, local storage and session storage behave differently, but none is exempt from consent. Learn how each one works, which to use and how to review them in your consent process.
October 22, 2026
9 min
Does reCAPTCHA Require Cookie Consent?
reCAPTCHA can be exempt as necessary security, but not every setup is. Learn how to assess your reCAPTCHA version, audit its cookies and keep forms working when visitors say no.
October 15, 2026
7 min